secretsofthedark

Google Dorks, Continued

I had been discussing the concept of Google dorks on the social network Misskey, and some people had said that the concept was unfamiliar to them. So let's dive a little deeper into this.

As explained before, Google dorks, also known as SQL dorks or Google hacks, are search terms that work on Google (and some other search engines) to find sensitive or confidential information. This sometimes includes such things as vulnerable login portals, passwords, SSH keys, social security numbers, names, and bank account information!

A recent dork shared by security researcher Ritika Keni was the following: inurl:pastebin “CVV”. Using this dork returns results containing credit card account details available on the web, which may or may not be valid. It is up to the researcher to sift through the results and figure out which ones work or not.

google dork pastebin results

Another one that returns interesting (and potentially harmful) results is:

site:*.blob.core.windows.net ext:xls | ext:xlsx (login | password | username)

As this dork specifies, it is searching for .xls and .xlsx (Excel) files that contain the text “login,” “password,” and “username.” So, as you might expect, many of the results have included spreadsheets with people's real names, usernames and passwords for things like Zoom. Given that numerous people are using Zoom for conferencing right now, this is something that should be alarming! Even more concerning are the spreadsheets that have personally identifiable information about people's locations, phone numbers, etc.

Back in 2018, IT Security Guru published an article entitled Is the bright web more dangerous than the dark? The term, which has only come into usage over the past few years, refers to information, like the types above, that are publicly available on the web and can be found with a quick search in many cases. In essence, while the dark web often gets demonized for its criminal activity and dark content, the clearnet contains just as much, if not more, personal information, and it does not necessarily have to be difficult to find.

Exploit DB has a much more comprehensive list of Google dorks which is continuously being updated by researchers, so if you want to try this out yourself, stop by there and test out a few from the list.

Here are some other examples you might want to try for fun:

site:pastebin.com intext:pass.txt “AutoCreate=TRUE password=“ “iCONECT 4.1 :: Login” “Index of /” +passwd “Index of /” +password.txt “Index of /admin” intitle:“webcamXP” inurl:8080 “not for distribution” confidential “mysql dump” filetype:sql site:.in inurl: admin login

If there is something to learn from this, it is also to go back and check any confidential information that you think might be publicly available and have it removed, if at all possible (though this can sometimes be a challenge too).

List of Privacy Respecting Services and Software (Ongoing)

User nikitavoloboev on GitHub had created a list of privacy-respecting services and software (originally in 2019) which provide alternatives to popular software developers such as Google, Microsoft, and Apple, as well as major social networks such as Facebook. Ironically, the original list is on GitHub, which is now owned by Microsoft, but it can be found elsewhere on the web as well. It's worth noting that there are quite a few alternatives to GitHub available too, which will be discussed further.

The list begins with corporate search engines such as:

  • Google - this one is obvious
  • Bing - Microsoft's search engine
  • Yandex - Russian version of Google, essentially

Search engines such as these track your searches and use them to serve you with ads and other intrusive features. For instance, you may notice that if you Google something like "baby clothing," then not long after, you will start seeing ads for baby clothing all over the web.

As alternatives, they suggest search engines such as:

DuckDuckGo – a search engine known for its privacy features. Startpage Qwant Searx – technically, this is a metasearch engine, not a search engine, but it will still achieve the same purpose.

It is worth noting that in the case of searx, as with the fediverse, there are many different self-hosted instances. Some of them can be found at searx.space. Several examples include searx.be, xeek.com, and searx.roflcopter.fr. The instances seem to vary widely in quality at times, however. For instance, on start.paulgo.io, an error message came up that read "Error! Engines cannot retrieve results: google ( Suspended: too many requests )." Even so, with searx, you can submit issues on the instance's git repository and try to have them fixed.

Also listed in the post are alternative social networks. Under "You are the product" are social networks like Facebook and Instagram. While not listed on the original post, Twitter (or as the fediverse calls it, "birdsite") should be included there as well. Facebook, in particular, is one of the most egregious offenders in the arena of privacy, given all the revelations that have come out about them in recent years, most recently the whistleblowers like Frances Haugen and others who followed suit.

Alternatives that they suggest are:

Scuttlebutt is a decentralized, P2P, open-source social platform.

Mastodon - Mastodon, which has been referenced on earlier posts, is also a decentralized social network, and part of the aforementioned fediverse. It uses the ActivityPub protocol, which is designed for federated (i.e. on interconnected servers) social networks. Like searx, Mastodon has many different instances, which are self-hosted. Examples include mstdn.social, mastodon.earth, and hellsite.site, among quite a few others. Each instance tends to have a different theme; for example, there are instances for artists, dads, hackers, and furries (or perhaps all at once in some cases).

Diaspora - Like Mastodon, Diaspora is also part of the fediverse, although it has a different type of UI/UX. Its feel is a bit more similar to Facebook, though without the invasive tracking issues.

Steem (Steemit) - Steem is a blockchain-based blogging and social media service

Indieweb - A community for building independent, open source social networks like those above

Minds - Minds is an alt-tech blockchain-based social network

Chttr - A "politically neutral" social network

Pleroma - Also part of the fediverse, Pleroma, like Mastodon, uses the ActivityPub protocol, though it has a somewhat different feel.

Cent - a democratized social network built on Ethereum

While the entire list won't be shared here, the rest of it also includes sections on email, operating systems, browsers, video sharing, and even AI assistants. Some of the OS's suggested are Linux, Tails OS, and Android with CopperheadOS; under browsers, they suggest such options as Firefox, Vivaldi, and Tor Browser.

Tor Browser

It should be noted that one social network not mentioned in the repository is Misskey, which is also part of the fediverse. Like Mastodon and Pleroma, it also uses the ActivityPub protocol, but it has many niche features, such as a Gallery, Chat, Games, and reactions. Some of the instances can be found at

EDIT: A few

What do you think? Are there alternatives to popular proprietary software that should be discussed here?

Update on the Twitch Leak from sizeof(cat)

The blog sizeof(cat), which covers similar subjects to this one, published an update regarding the October 6 Twitch leak, including some additional information.

The full text of the leak can be found in this torrent magnet: Torrent (128GB): magnet:?xt=urn:btih:N5BLZ6XECNEHHARHJOVQAS4W7TWRXCSI&dn=twitch-leaks-part-one&tr=udp%3A%2F%2Fopen.stealth.si%3A80%2Fannounce Repository listing: https://dpaste.org/MvoM

If newer information comes out about the leak, it will be mentioned here as well. Stay tuned!

Entirety of Twitch Data Leaked

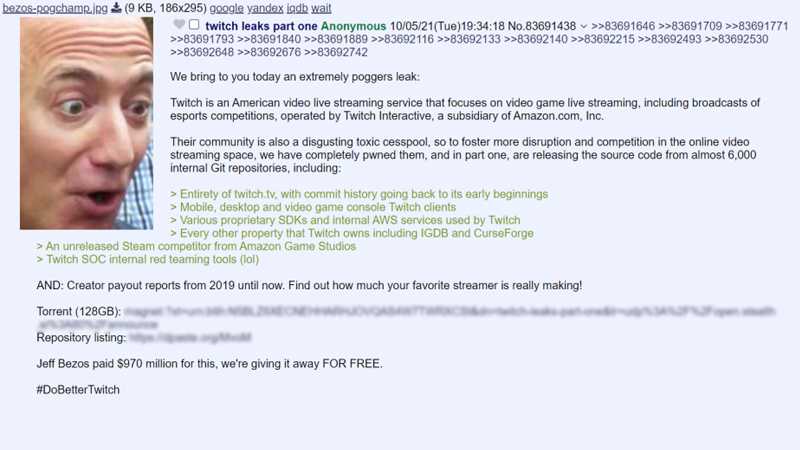
A 4chan user has just leaked the entirety of Twitch's private data, including source code, various user account details, payout data, and stream keys.

4chan Twitch leak post

Also reportedly included in the leak is data from a yet-unreleased Steam competitor. Other details that have been released, according to the 4chan post, consist of:

  • 3 years worth of user payout details
  • All of twitch.tv, "with commit history going back to its early beginnings."
  • Source code for all clients, including mobile, desktop, and video game consoles.
  • Code from proprietary software development kits (SDKs) and internal AWS services used by Twitch
  • Other data from Twitch properties such as IGDB and CurseForge
  • Twitch's internal security tools

Of further concern is the fact that this leak has been labeled “part one,” which implies that future leaks will be released. While the initial leak has not included password data, based on similar data breaches in the past, it is reasonable to assume that passwords may be included in future parts of the leak, if such data exists. Hence, Twitch users are encouraged to change their passwords immediately and enable 2FA, if not delete their accounts altogether.

The user who posted the leak stated that one of the motivations behind it has been Twitch's failure to curb hate speech, misogyny, and other malicious actions prevalent on the platform.

What are Google Dorks? (Examples Included!)

Google hacking (also known as Google dorking or SQL dorking) is a technique whereby coders and pen testers find vulnerabilities and sensitive information using Google searches. This sometimes works with other search engines as well, like DuckDuckGo, Bing, and Startpage, although given that Google is the most popular search engine in the world, it tends to find the most results.

Though dorking is not a new concept (it dates back to 2002 when a hacker by the name of Johnny Long began collecting the results of Google searches that revealed system vulnerabilities), it is still relevant today.

These results of these dorks can include such things as usernames, passwords, IP camera login details, and vulnerable files. Part of what is so fascinating about these dorks is that they do not require sophisticated software or hardware; the information is just sitting out on the web publicly.

One example of a Google dork is the following: +”:8080”;+”:3128”;+”:80” filetype:txt – This searches for lists of proxy servers using the ports 8080, 3128, and 80, some of which are good for anonymity. The results show up as text files, as indicated in the search terms.

google dorks list

Other dorks include such searches as:

    intitle:"webcam" "login" - finds login portals for webcams intitle: "index of ftp passwords" - finds passwords for FTP servers site:".edu" intitle:"admin login" - finds .edu sites, some of which contain admin login portals intitle:index.of inurl:grades site:edu - finds school databases with students' names and grades

Granted, not all of these dorks return useful results at times. The vulnerabilities that they point to may have been patched, but if you search long enough, it is likely that you will find something. Even the searches that seem mundane, such as the login portals, often have vulnerabilities. In some cases, all it took to log into these sites was the username “admin” and the password “admin” as well!

If you are interested, a more extensive list of these dorks can be found at Exploit Database: Google Hacking Database. This database is continually updated by pen testers, so you can check back frequently to find new ones.

Even without finding something interesting in the database itself, you can play around with potential dorks to see what might be sitting out on the web. For instance, try variations on “site:https://docs.google.com/" with different words at the end of the URL, such as “password,” “username,” or “passport number.” It is surprising how much of this sensitive information is publicly available for anyone to see. The reason for it being there, however, is probably that whoever added the info to a database in the first place was unaware that it could be seen by anyone merely doing a Google search.

For example, one of the results that came up when dorking docs.google.com was a list of default usernames and passwords on Wi-Fi routers. Were someone able to get to the login portals for these routers, they could essentially log in as an administrator.

The internet of things (IoT) search engine Shodan was designed for searches like this, and sometimes finds similar vulnerabilities. One search that works on Shodan is “has_screenshot:true,” which frequently shows screenshots from vulnerable IP cameras or Windows computers that use Remote Desktop Protocol. The latter provides a GUI for users to connect remotely to another computer over a network connection, but has the unfortunate drawback of creating an exploitable security vulnerability.

Windows Remote Desktop Protocol login

Try fooling around with some of these yourself and see what results come up. The information you find is sometimes unnerving, or even frightening, particularly if it's your own!

Internet Mysteries: What was Mortis.com?

Those of you who follow internet mysteries may be familiar with a strange site called Mortis.com. Originally registered in 1997, its landing page had nothing but the name mortis.com, along with username and password fields. No archives of the site exist today, not even on the Wayback Machine, but some looking into the mystery recreated the image of the login page:

mortis login page

According to some coders who attempted to crack the login, it was extremely difficult to get through, and it is not publicly known if any were able to figure out the username and/or password. The mystery is described in more detail on this Reddit post on r/UnresolvedMysteries:

So awhile back I stumbled across this internet mystery while researching lakecityquietpills.com and came across and equally intriguing internet mystery related to a mysterious website called mortis.com. Apparently this website when it was active, it was created in 1997, as it has long since been shut down, Came up with a login and password screen that according to some experts was extremely hard to hack into. with some resorting to using brute force applications and having little to no luck in getting past the login screen. It got a lot weirder the more people started looking into it, because more and more weird connections and Links started being made with this website.

Apparently, according to the post, large Usenet files were linked back to the website, including one that was 39GB in size, which only added to people's curiosity about what was behind it. Contrary to popular belief, Usenet is still around today, even though larger forums and social media networks have surpassed it in popularity.

Adding to the mysterious nature of Mortis is that almost all references to it have been removed from the internet at present, including an archive on the Wayback Machine. Obviously, this has only fueled internet investigators' interest in the site.

Some of those looking into the mystery traced the site's ownership back to an individual named Thomas Ling, who also owned several other domains registered in the late '90s and early '00s, such as:

These are no longer online, though they can be found on the Wayback Machine. Most just have a picture of a black chess piece on a black background, and nothing more. It appears as though the chess piece image was just a placeholder, and the creator of the site intended to update it later on.

Oddly enough, at present, there is a new site called mortis.cc, which looks very similar to the original: black background with a login field asking for a username and password. It is not publicly known if the new site has any relation to the original, or is just a clone made by someone interested in the mystery.

mortis.cc login page

It would be interesting to see if anyone can crack the login for the new site as well, though if it is affiliated with the original, that may also be difficult. One theory that people have had about Mortis.com is that it was some kind of P2P filesharing site, especially considering the Usenet connection. Given that other such sites have been shut down by lawsuits, this would be an unsurprising answer.

So, then, what do you think mortis.com was for? Is the new site related to it in any way, or is it merely a “fan site” made by someone interested in the mystery?

I Was in the Epik Data Breach

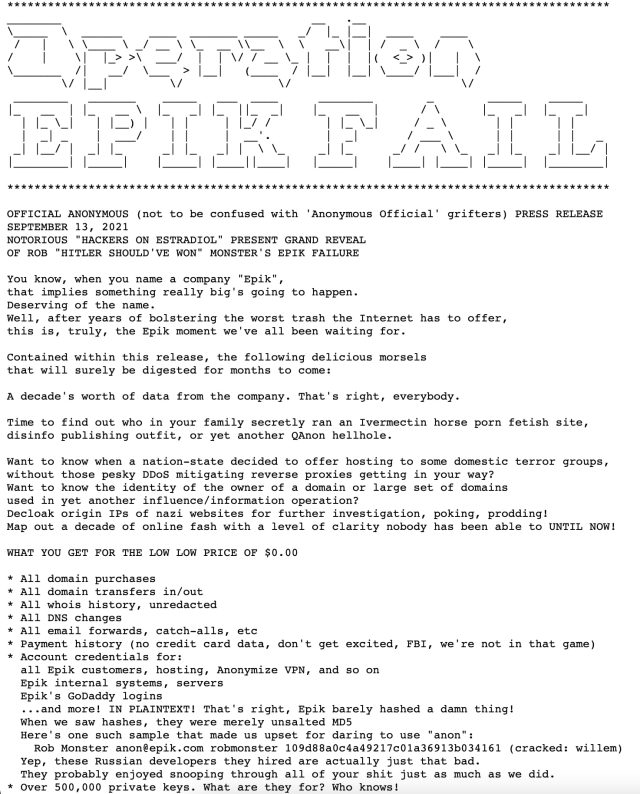
Yes, it's true. I was informed the other day via email that my name and some of my personal information was among the many in the Epik data breach released on September 13, which included members of Parler, Gab, 8chan, and other sites. This may require some explanation, however.

Epik data breach note by Anonymous

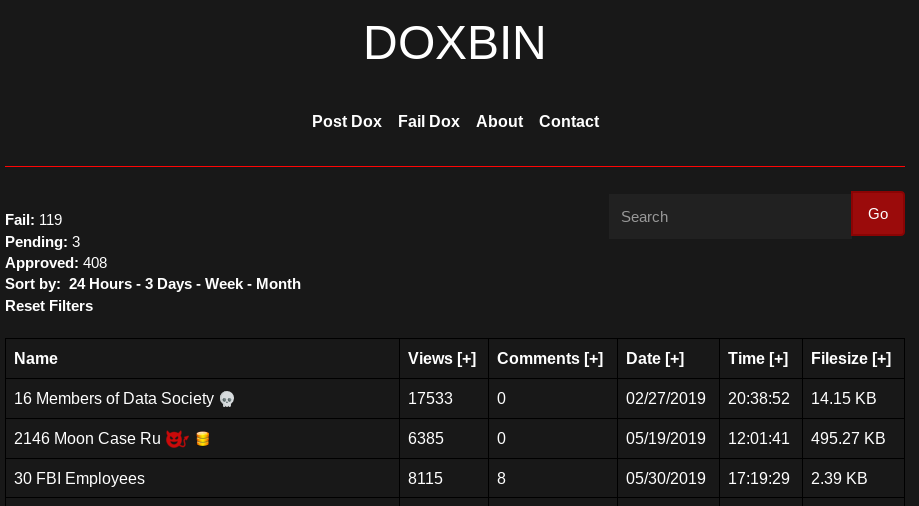
I am not affiliated with any alt-right groups, but back in 2019, I had been doxed by a member of Deadnet, the former owners of the site Doxbin. Among the information in the dox was my real name, address, phone number, social security number, and some of my usernames and passwords. The reason they did so in the first place was that I had written a post about them on my old WordPress blog, and they took it as a dare. Brian Krebs wrote some interesting articles about the group, including Neo-Nazi Swatters Target Dozens of Journalists.

Doxbin front page

After the Deadnet users had posted my details on Doxbin, a few of them proceeded to crack some of my passwords on social media accounts, swat me, etc. As a result, however, this propelled my interest in cybersecurity, at the very least. It has made me aware that no matter how “safe” you think you are, there are probably still holes in your security and anonymity somewhere. It could be something as simple as using a VPN service that has easily exploited vulnerabilities, which then gives the attackers access to your machines, or inadvertently revealing your mother's maiden name, which is the answer to a security question on your bank.

So, despite this revelation about Epik, I have reached the point where it doesn't surprise me much anymore, and if I make a security faux-pas, that is an opportunity to learn how to patch it. It seems that one can never get too comfortable, security-wise, because that's when someone will exploit whatever vulnerabilities exist. There is still much to learn, so I am going about the process of doing so.

What are Some Alternatives to ProtonMail?

Those who keep up with privacy news have probably heard about ProtonMail handing over the IP addresses of some of its users to Swiss law enforcement in the recent case, prompting a lot of criticism from those in the community.

If you read the article above, however, ProtonMail says they were forced to comply with the order and could not appeal. Their suggestion to users was to use their Tor hidden service, which also obfuscates IP addresses in a way that ProtonMail itself cannot.

There are, of course, other email services that are similar to ProtonMail, in that they are (ostensibly) privacy-focused, but no email provider can be trusted 100%, unless you set it up yourself. People have discovered the same issues regarding VPN providers that claim not to keep logs as well, particularly in cases when law enforcement subpoenaed them to hand over a user's data.

Part of the issue is that email, in general, is not the most secure form of communication, as email messages are easy to intercept. A post on StackExchange explains some of the reasons behind this:

Emails can be sniffed in transit, since they are not encrypted (some sites will opportunistically employ encryption for transit, but this is not reliably activated).

Emails will be stored on physical disks in the servers which are involved in the operation: the sender's email server, the recipient's email server, and any server “in between”. Physical disks can be sniffed when decommissioned or through backup tapes. Bored interns in the facilities managing these servers could simply have a look.

It is easy to make emails go to the wrong machine by altering the DNS. There are viruses which routinely inspect emails received by infected machines, in search for passwords, credit card data or other juicy information.

The whole email system just assumes that everybody is honest and nice and trustworthy. It is surprising (but morally encouraging) that it works at all.

A similar situation occurred with a provider named Hushmail back in 2007, and the Reddit post Hushmail: A cautionary tale of trusting webmail providers like Protonmail summarizes this situation a bit:

Before Protonmail or Tutanova [sic], or whatever the flavor of the month 'secure' webmail snake oil provider is, there was Hushmail, which similarly offered “secure” and “encrypted” webmail, claiming that “not even a Hushmail employee with access to our servers can read your encrypted e-mail, since each message is uniquely encoded before it leaves your computer”.

hushmail logo

And then court records showed that Hushmail handed over several CDs-worth of emails to the US (Hushmail was based in Canada):

On June 6, 2007, DEA SA Shawn Riley received three CD'S via Fed Ex from the DEA San Diego Division Office. The CD's were the results of a mutual legal assistance treaty (“MLAT”) executed on Hush Communications Inc, based in Canada, for email addresses [Hushmail email addresses]. Hush Communications Inc., also known as Hush Mail, is a free encrypted email communication system that claims to ensure the security, privacy, and authenticity of emails sent and received by it's users.

The results of the MLAT conducted on [Hushmail email address] included an IP log associated with access to this e-mail account.

In the same sense as putting your trust in a VPN provider, you are relying on a third party to protect your data, even if they claim to have a “privacy-centric” or “anonymous” service. Additionally, the mere fact that a company advertises itself as being more private usually makes it a target for attackers.

Still, better options exist: sn0w, admin of the Pleroma instance cofe.rocks, suggested encrypting emails with PGP, as well as using either Mailbox or